-
Welcome & Breakfast
Done
-
Apéro
Done
-
Welcome & Lunch
Done
-
[Keynote] From Signals to Responsibility: What Security Really Means Now
Anna MempelDone
-
Coffee Break
Done
-
[Panel Discussion] The Era of "Agentic" AI
Anna MempelDone
-
Coffee Break
Done
-
[Keynote] Operating at the Edge of Chaos: The CISO Lessons the War Forced Upon Us
Olivier BusoliniDone
-
Dinner
Done
-
Coffee Break
Done
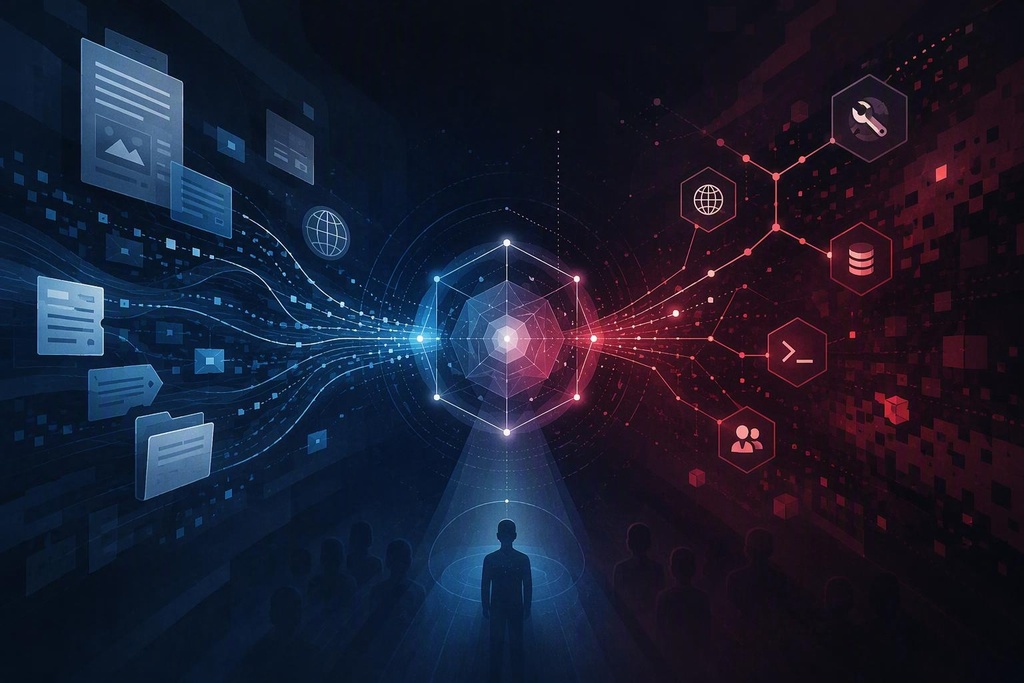
Prompts, skills and agents - a reality to check on why it starts with education.
An agent is not a chatbot with better manners. It reads content nobody reviewed, calls tools through MCP servers, and acts on behalf of employees — with their permissions. The attack surface shifts: the PDF, the ticket, the web page become the command line.
This talk uses examples to show how indirect prompt injection works, why the combination of data access and untrusted content is the real danger zone, and what risks MCP integrations bring: over-broad permissions, poisoned tool descriptions, unvetted community servers, missing auditability.
The uncomfortable point: there is no patch. No filter reliably tells user intent from data. What remains are architectural decisions — and people who understand what they are deploying. Agent security starts with education, not with the SOC.